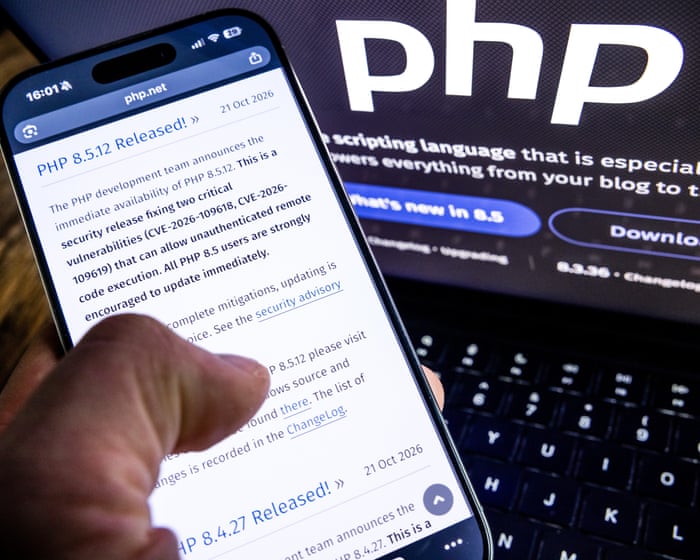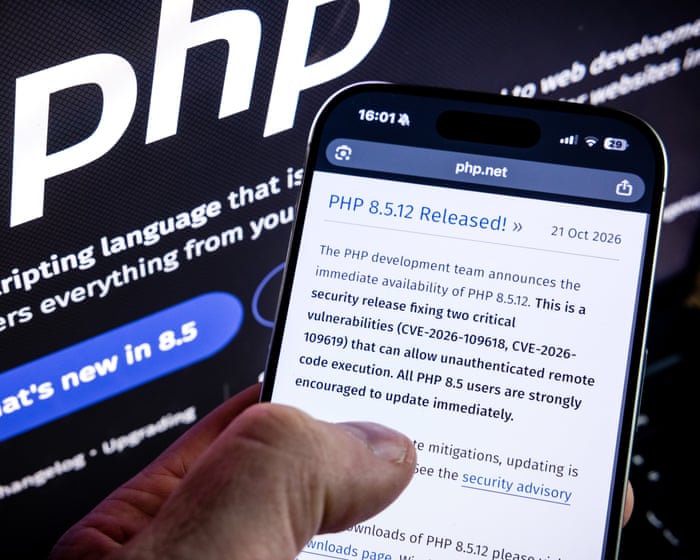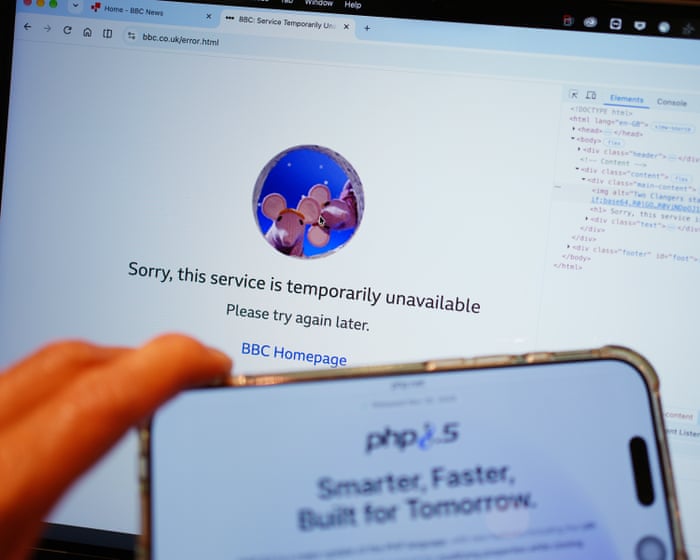
Websites globally are facing a massive wave of security threats as malicious actors launch millions of automated attempts to exploit a severe vulnerability in the PHP programming language, according to Business | The Guardian. The high-volume attacks have forced both corporate networks and government entities to take drastic action, including pulling web portals offline entirely to install urgent security patches.
PHP serves as the digital foundation for a vast majority of the internet, powering approximately 70% of all sites online. Because of this widespread ubiquity, the sudden discovery of a critical code flaw has triggered an unprecedented scramble among system administrators. As digital defenses race against automated exploit tools, understanding the technical nature of this emergency is vital, leading many to examine what PHP is and how bad the computer language flaw is as organizations struggle to contain the fallout.
Global Fallout and Mitigation Efforts
According to the report, the scale of the incident has caught many digital infrastructure teams off guard. Rather than risking data breaches or system takeovers, numerous enterprise operators and public sector agencies chose to disconnect their servers from the public internet entirely. This emergency downtime aims to give engineers a secure window to apply necessary software updates and verify system integrity.
The widespread disruption highlights vulnerabilities in foundational web technologies that millions of businesses rely on daily. For a deeper look at how this crisis unfolded across international borders, readers can consult our previous reporting on the flaw in the PHP computer language that led to global website shutdowns. Security analysts continue to monitor server logs as organizations try to determine the full extent of the attempted intrusions.
Analysis: Why This Matters and What Lies Ahead
(Context: This section provides analytical depth regarding the broader implications of the security event.)
The current crisis underscores the fragile nature of modern digital infrastructure, where a single coding flaw in an open-source language can jeopardize a significant portion of the global web. When core components like PHP are compromised, the stakes extend far beyond temporary downtime, threatening sensitive user data, e-commerce transactions, and essential public services. Small and medium enterprises, which often lack dedicated round-the-clock cybersecurity teams, remain especially vulnerable to prolonged outages and potential data exfiltration.
(What to watch: Observers should monitor whether patch adoption rates outpace the spread of automated malware scanners. Regulators may also face renewed pressure to mandate stricter security baselines for open-source dependencies used in critical public infrastructure.)
Sources: Business | The Guardian